Forum Discussion

Improvement: Handling Component Installs for Vulnerability Assessment
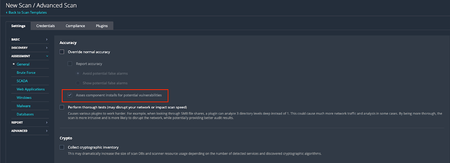

My apologies A-GoodSloth - confirming this feature is now available in Tenable SC - no version update required.

Can someone please confirm that this is indeed working as it should for tenable.sc ?
From our experience being on tenable.sc 6.8.0, we can see the new "Is Component" reporting within our respective plugin reporting but we don't get all the results unless we're running Paranoid scans.
- rmoody7 months agoProduct Team
Hi george_mentetak ,
Yes, this appears to be working in SC v6.8.0. Please make sure that the scanner has both its plugins and templates updated to the latest (SC should handle this for managed scanners).
Can i ask, which vulnerabilities (plugins) are missing in your normal scan reports - i.e plugins you feel should not require paranoid mode? Please attach a scan result (diag scan DB) if you are comfortable doing so here, or else you can always log a ticket with our tech support team if needed.
- george_mentetak7 months agoConnect Contributor
I can confirm that we are using the latest, i.e. Plugin Set 202603230317 and Policy Template Version 202603191049 yet unless we're running Paranoid scans, we don't see the Curl (240632, 30277, etc), OpenSSL (266297, 296297, etc) ones as an example.


