Forum Discussion

Improvement: Handling Component Installs for Vulnerability Assessment
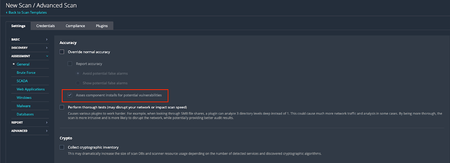

rmoody Did this get reverted again? I have a long running support ticket and have done a lot of debugging. We are not accurately detecting component and managed detections and now told once again we need to enable paranoid scans.
To community: does anyone else notice that this no longer works again? SQLite and LibCurl are not accurately flagging and also require paranoid checks that are not documented as needing to be enabled. ... Why is Tenable constantly moving the goal post here?! We are being told to setup another whole new scan policy and scans to detect component and managed installs, that managed installs require paranoid checks now.
Tenable plug pages for these plugins says Paranoid does not need to be enabled, but support says it does. We see also that component checks is not reliable. Ontop of it it seems like these plugins for LibCurl and SQLite superseed one another and dont acuratly show the same detctions from one version to another.
Example the current plugin (newest) doesnt show the same detctions as previous version. But when both are enabled only the newest runs. Ok superseed it seems, no way to see this cause tenable doesnt show that info, but I expect to see the previous findings show for the supersceed plugin and we dont. Tenable is creating a major False Negative rate here. For a vulenrabiltiy detecion company that is REALLY BAD.
Plugin 342617, 342615, 303594, 321188
-Ashman
 dominik_raum3 days agoConnect Contributor III
We also receive answers from support to use paranoid checks & also include path options when we notice that some detections work on systemdrive but not found on other drives for some plugins while other plugins work without these extra triggers, which is quite annoying in thorough mode. It became a fully non-transparent process.
We constantly forced to write our own search scripts to find possible vuln's everywhere because Tenable Plugins filter out so much circumstances that they miss alot positives. I wish there would be a scan mode that does a real full scan across all local drives, with options to minimize the filtering.
For example fully working Tomcats that are found on the system are right now not on the Tenable radar, because the plugin filters them out if they have a missing uninstall string in the registry. Oh well..


